Hack'n Speak est un podcast francophone consacré à l'univers du hacking et de la cybersécurité. Son objectif est de donner la parole à des hackers pour qu'ils partagent leurs outils, leurs recherches et leurs expériences. Chaque épisode explore des sujets techniques et pratiques liés à la sécurité informatique. Le podcast s'adresse aux passionnés comme aux curieux qui veulent mieux comprendre le milieu du hacking.
Épisodes
0x38 Mizu | Recherche de 0days et XSS dans dompurify
Kevin Mizu website https://mizu.re/RCE wordpress: https://wp2shell.com/Twitter Mizu https://x.com/kevin_mizuTwitter mpgn https://x.com/mpgn_x64

0x37 lgandx (Laurent Gaffié) | De l'IA pour le pentest, whatsapp IA, un conseil (partie 2)
https://blog.secorizon.com/2026/05/meta-whatsapp-private-processing.htmlhttps://secorizon.com/secorizonaiTwitter mpgn https://x.com/mpgn_x64Twitter secorizon https://x.com/secorizon

0x36 lgandx (Laurent Gaffié) | Responder, Secorizon, de l'IA (partie1)
Site web https://secorizon.com/Twitter secorizon https://x.com/secorizonTwitter mpgn https://x.com/mpgn_x64Ban github/gitlab https://cybernews.com/security/github-bans-researcher-releasing-windows-zero-days/

0x35 Podalirius (Rémi GASCOU) | L'open source, SpecterOps, l'IA
https://podalirius.net/fr/https://x.com/podalirius_/https://www.youtube.com/watch?v=-7WM16i3FG0https://specterops.io/
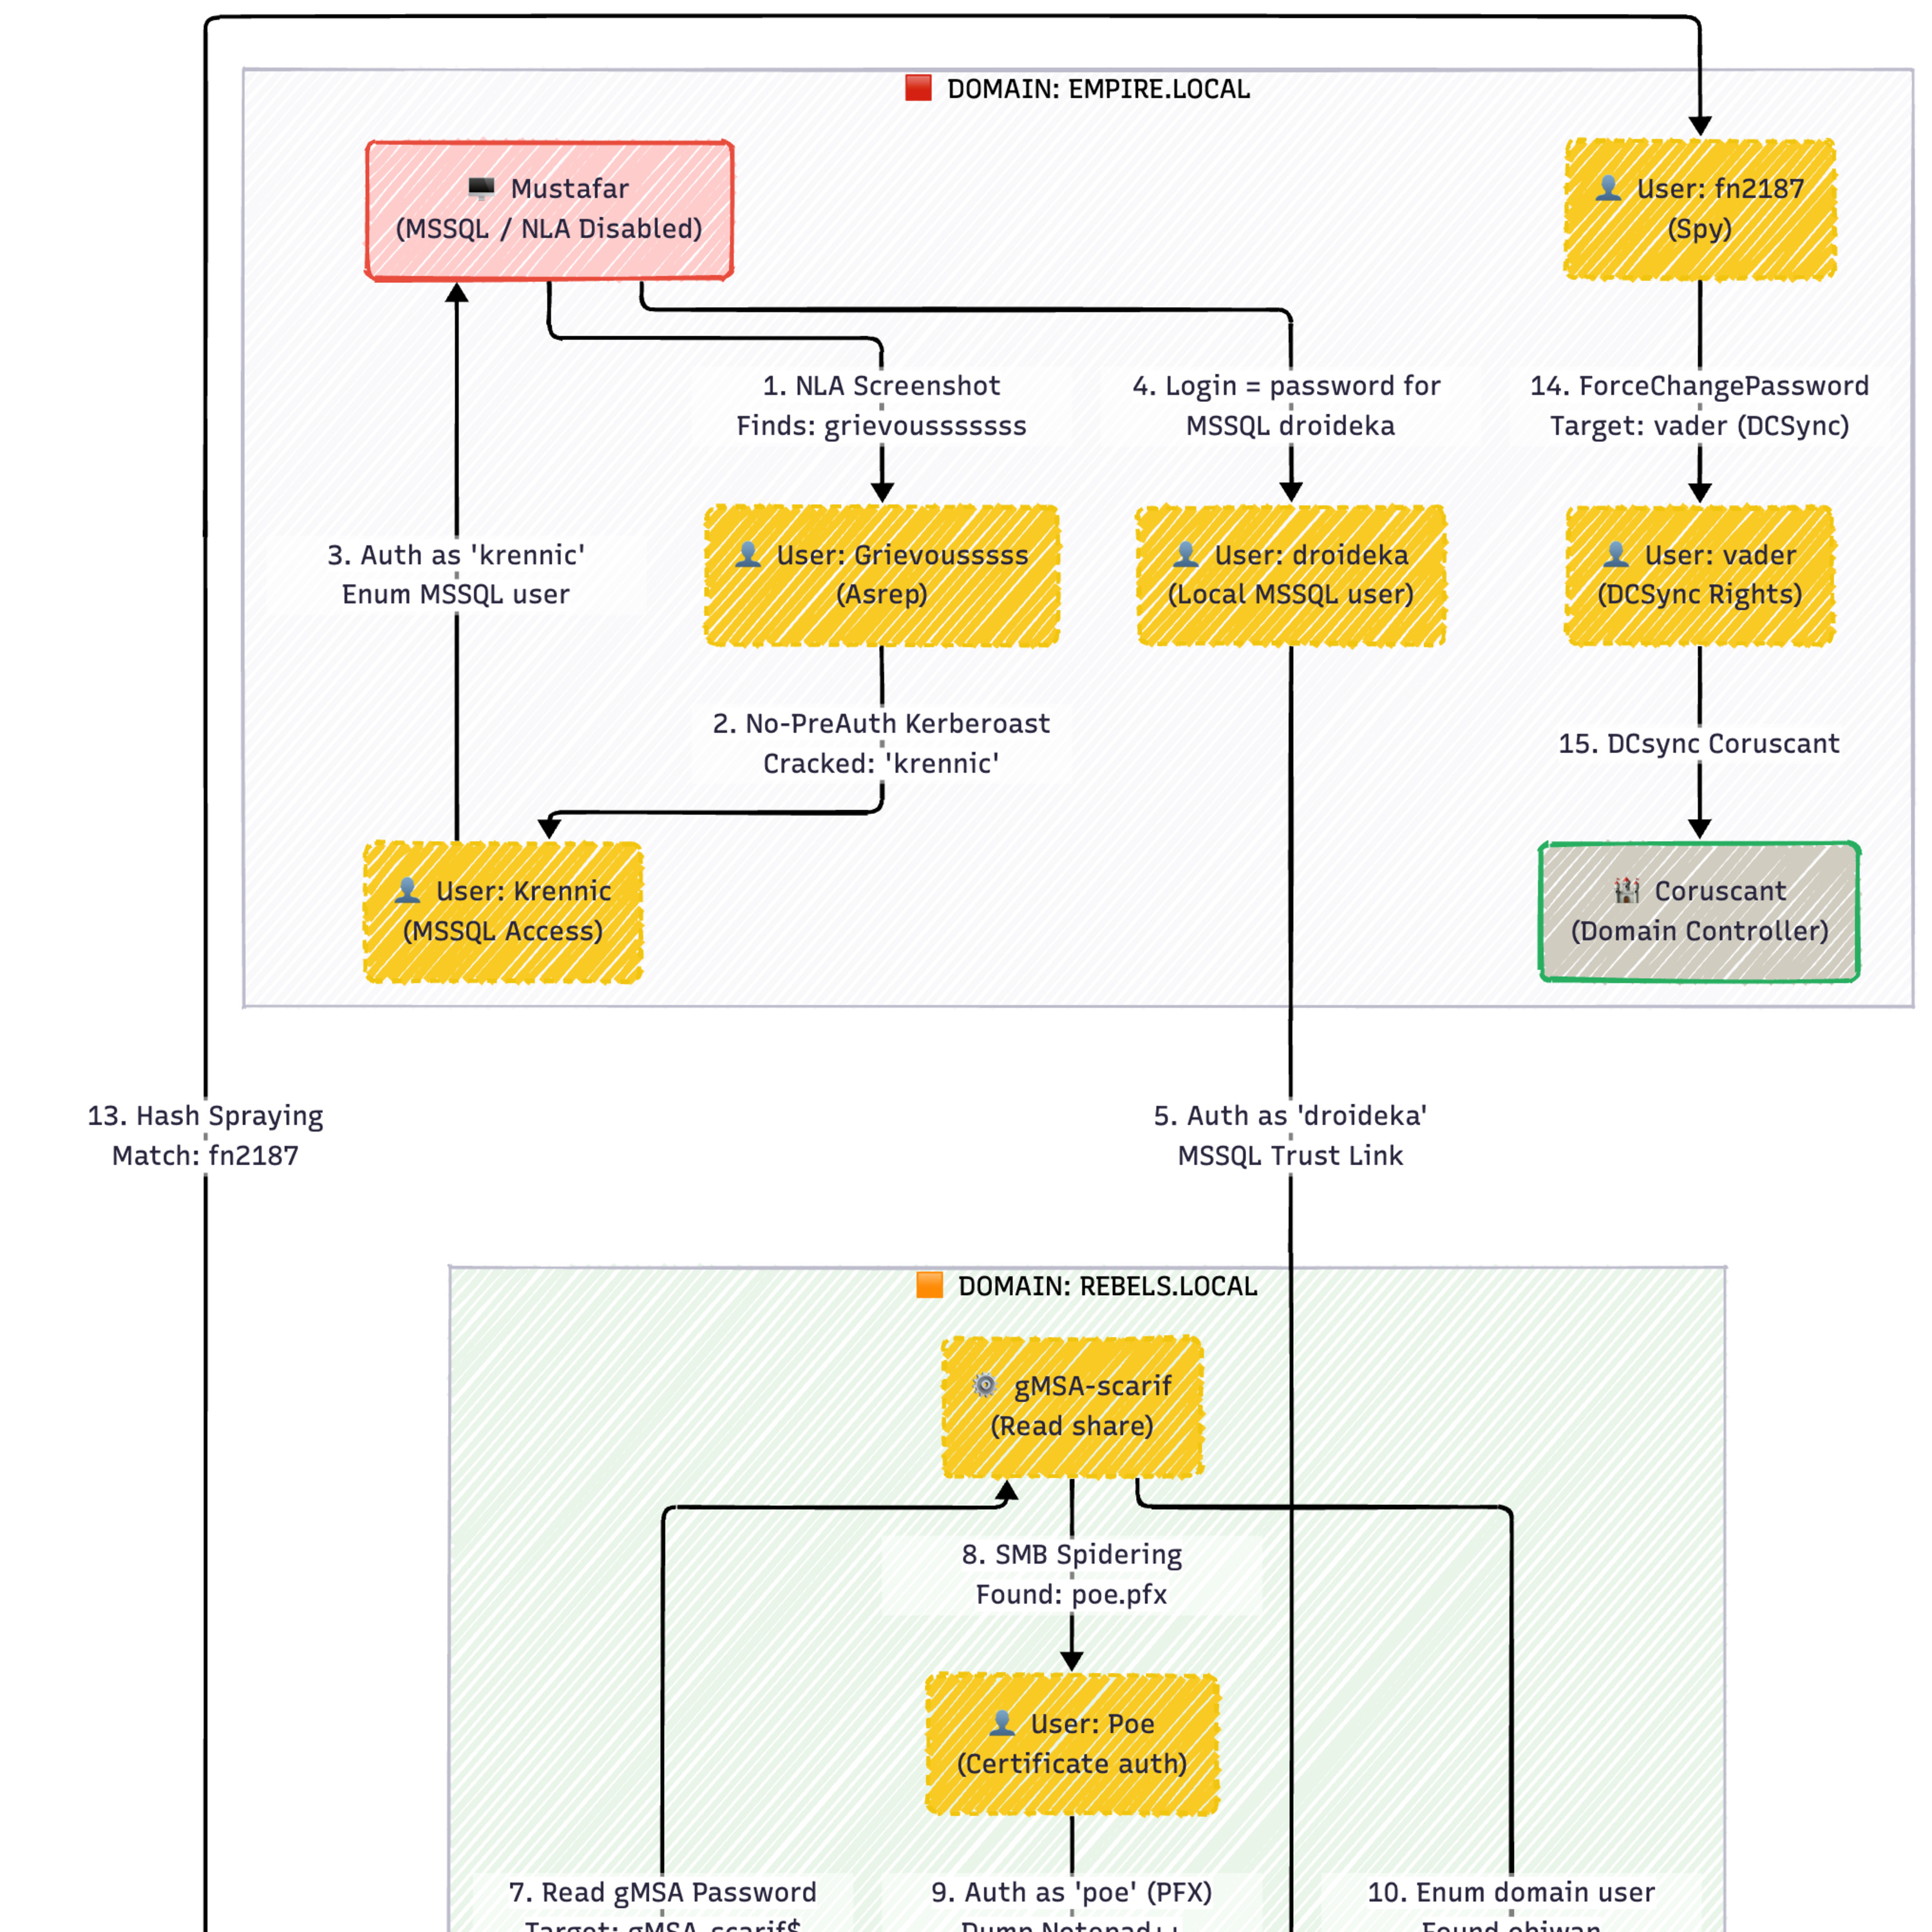
0x34 Workshop NetExec LeHack 2025 (3/4)
https://github.com/Pennyw0rth/NetExec-Lab/tree/main/LeHack-2025https://blog.anh4ckin.ch/posts/netexec-workshop2k25/https://lehack.org/2025/tracks/workshops/#active-directory-pwnage-with-netexec
0x33 Zwindler (Denis Germain) | Du Kubernetes, de la sécurité, une anectode
blog: https://blog.zwindler.fr/Le post mortem de datadog https://www.datadoghq.com/blog/engineering/2023-03-08-deep-dive-into-platform-level-impact/Ciel ! Mon Kubernetes mine des bitcoins !https://www.youtube.com/watch?v=RbqHDpoaqR8Livre 50 solutions pour les postes de dev et les clusters de production https://50ndk.zwindler.fr/
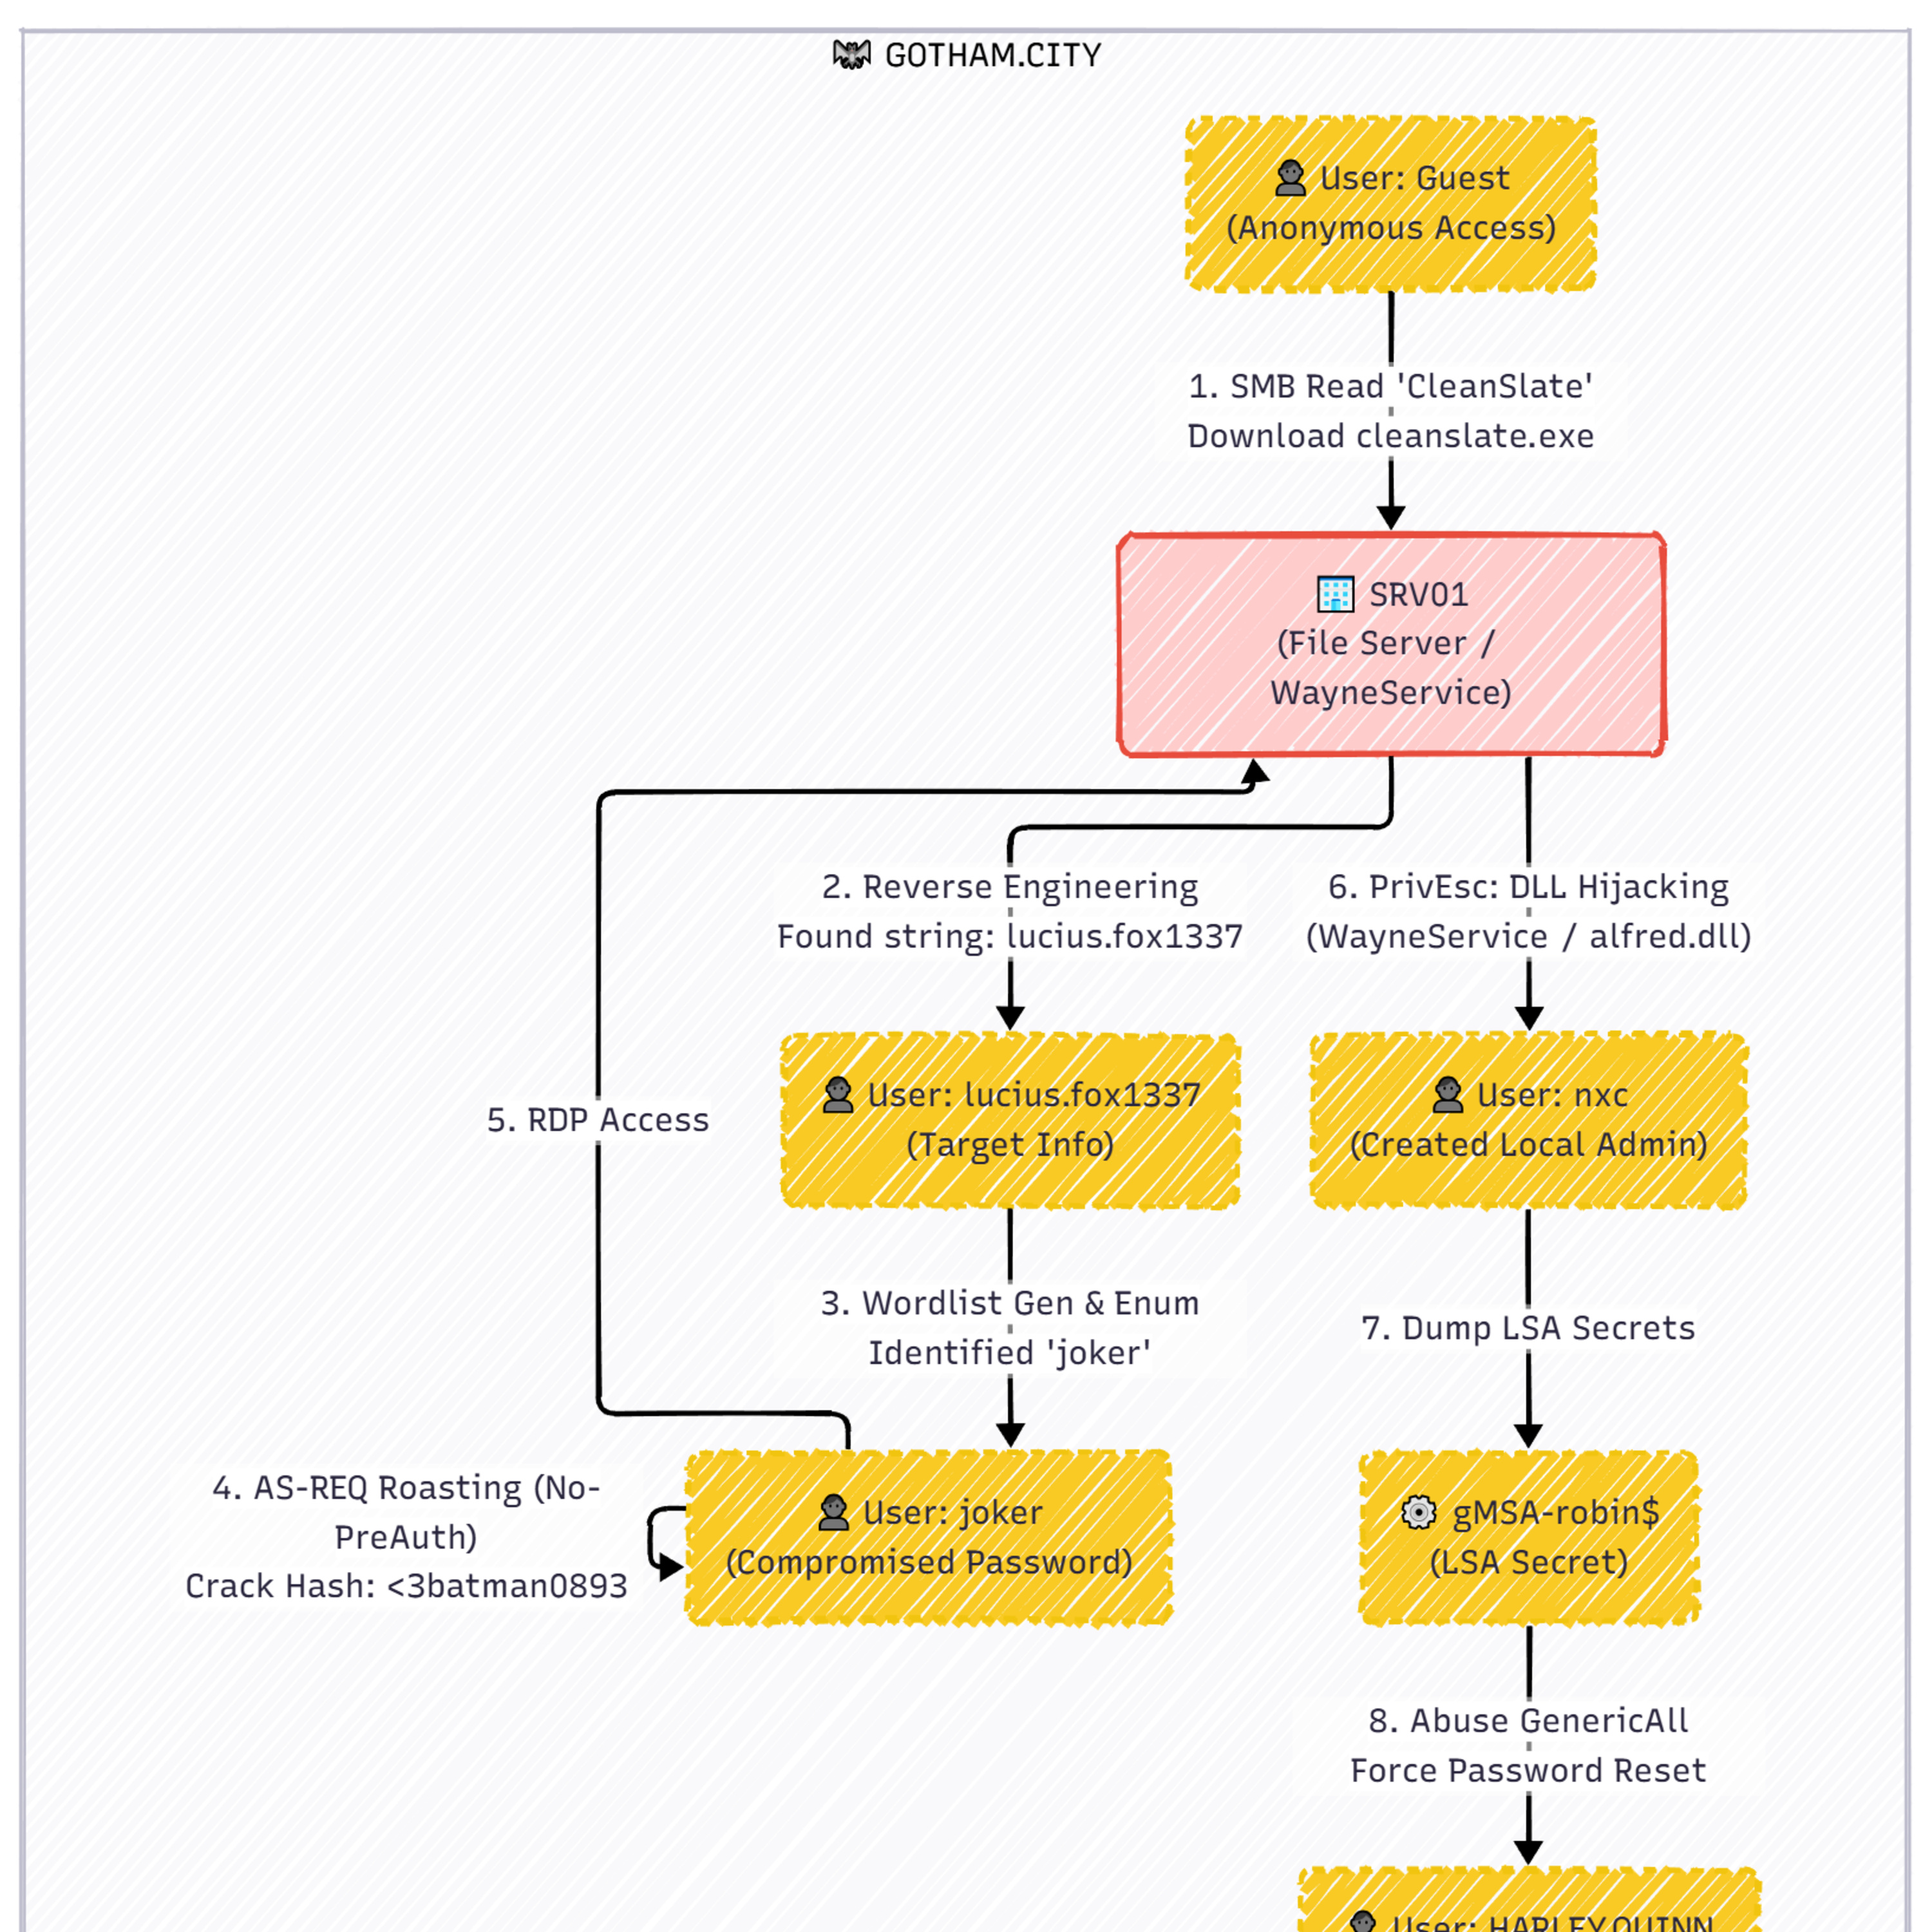
0x32 Retour sur le CTF Active Directory Windows Barbhack (2/4)
Github https://github.com/Pennyw0rth/NetExec-Lab/tree/main/BARBHACK-2024Writeup from Acceis https://www.acceis.fr/write-up-barbhack-challenge-active-directory/Twitter: https://x.com/mpgn_x64Ludus https://docs.ludus.cloud/docs/environment-guides/barbhack-ctf-2024
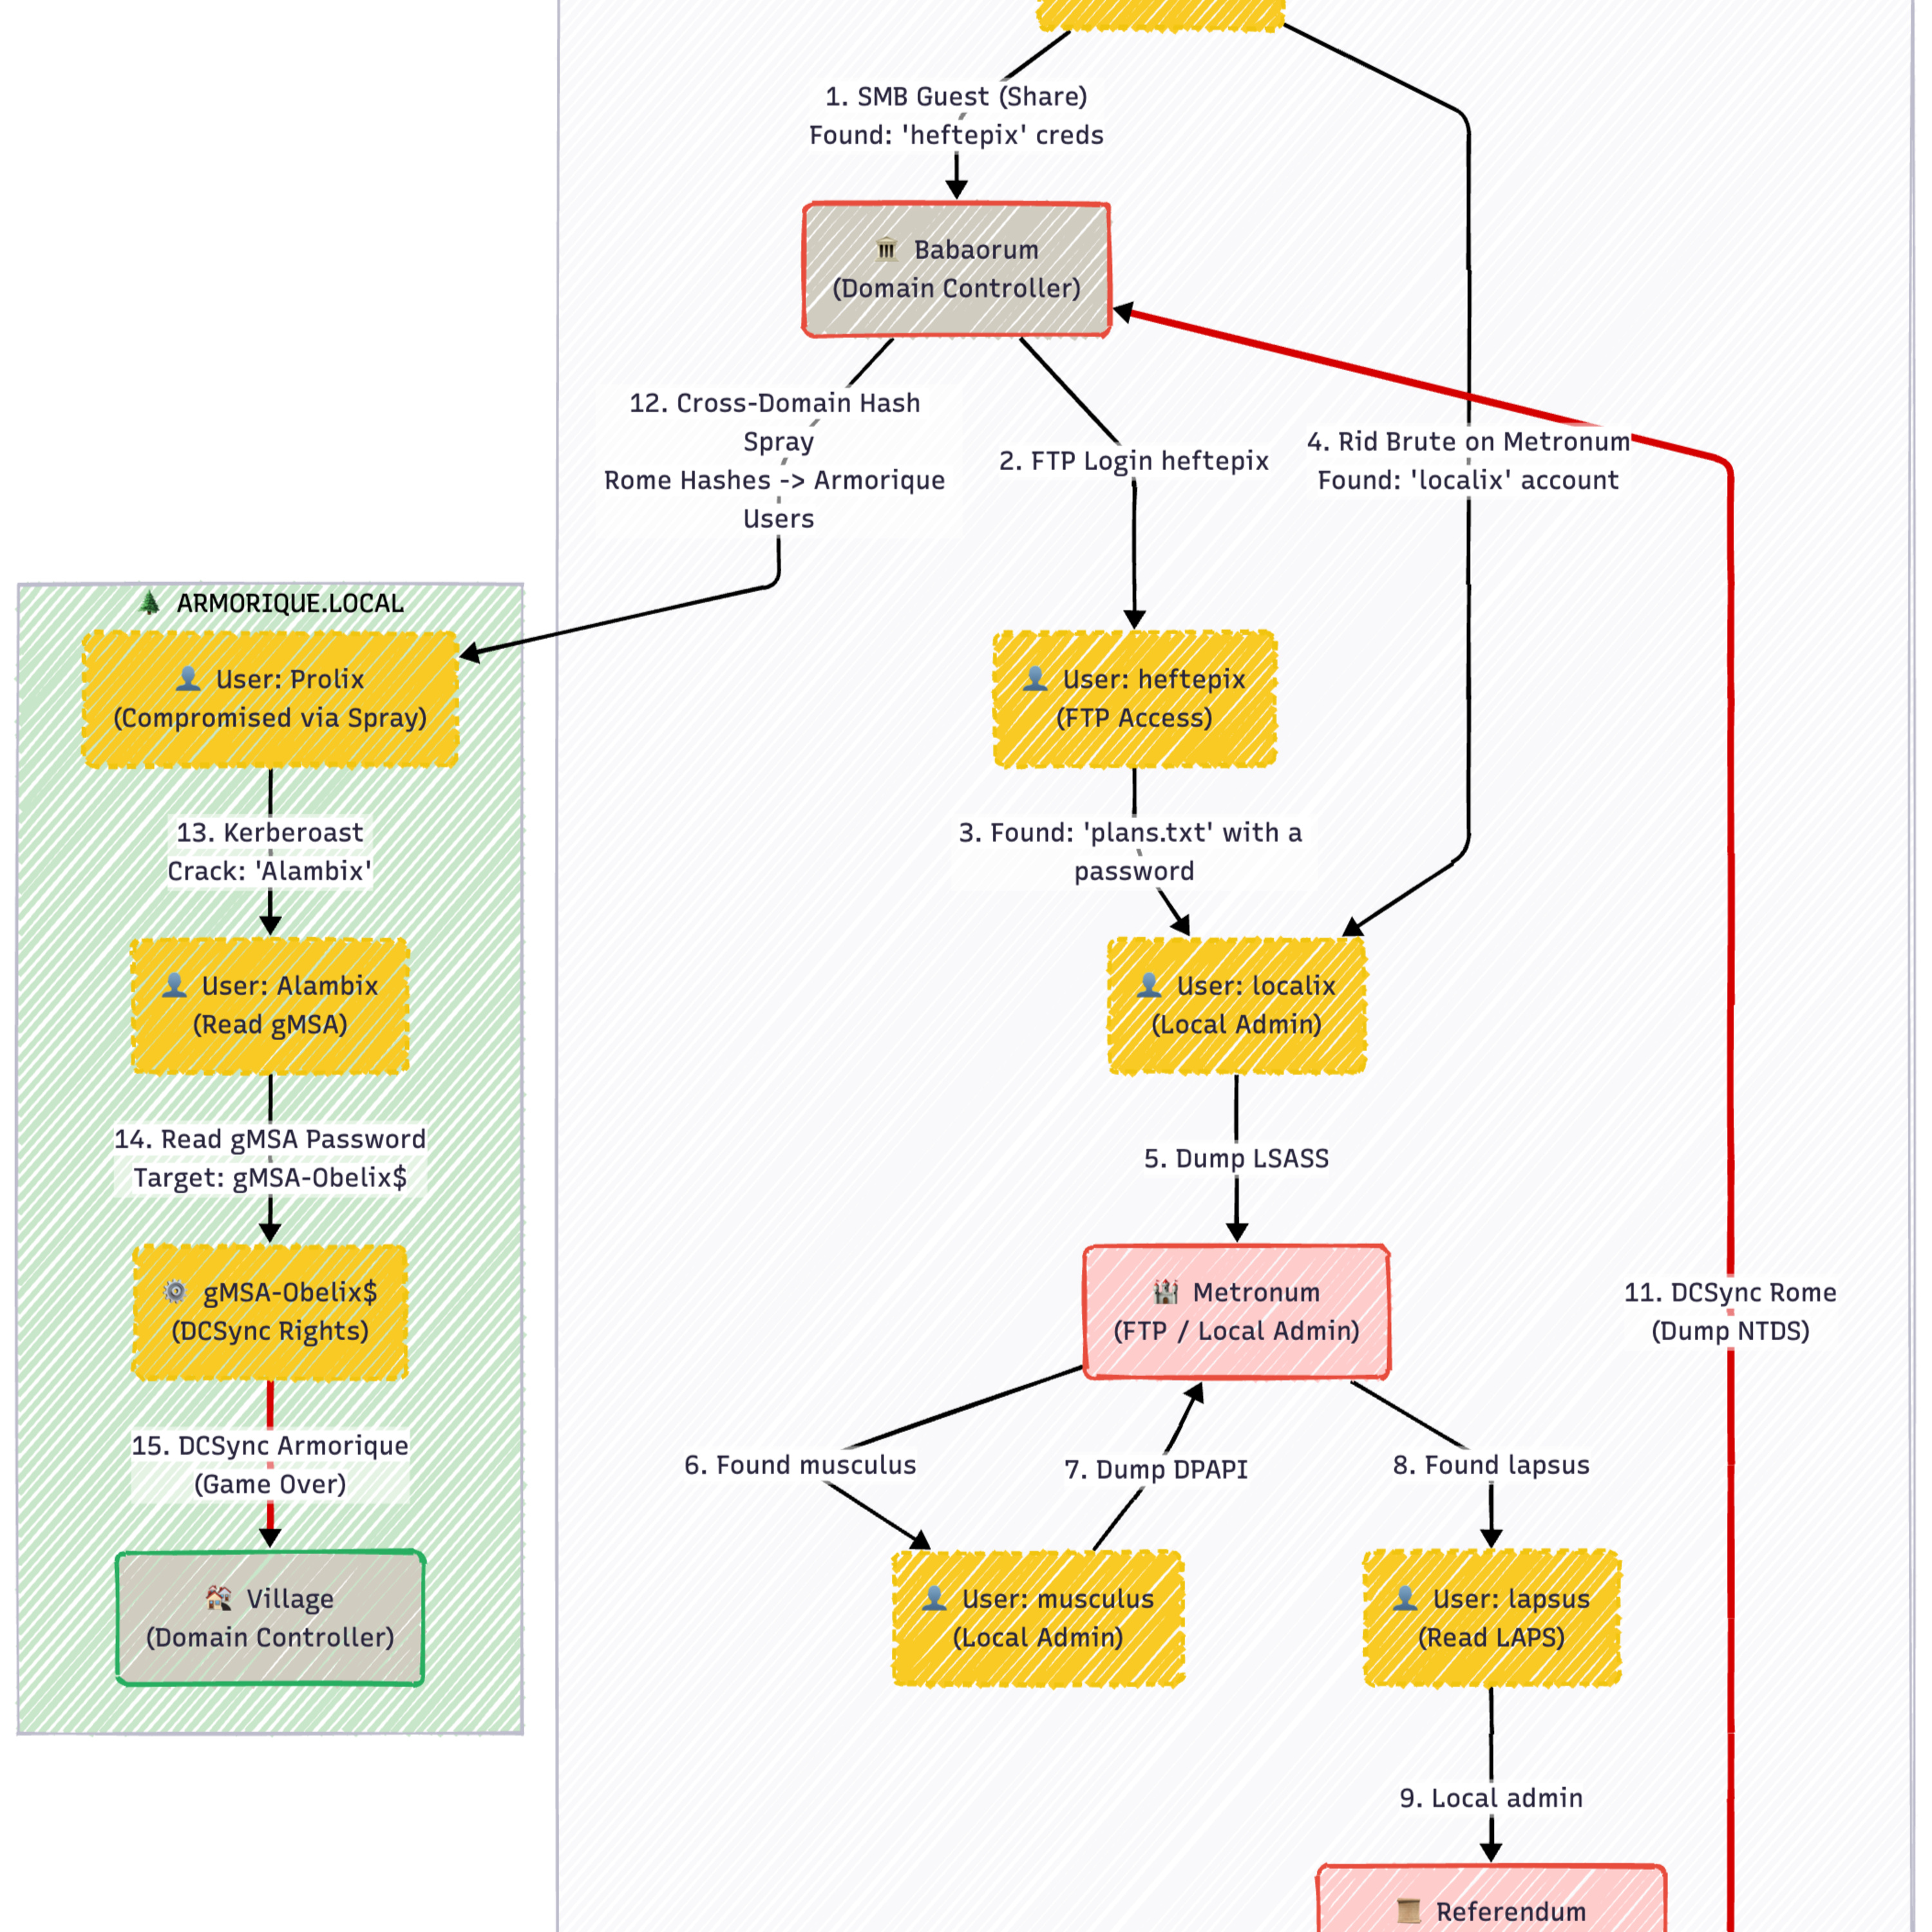
0x31 Retour sur le workshop LeHack-2024 (1/4)
Github https://github.com/Pennyw0rth/NetExec-Lab/tree/main/LeHack-2024Writeup from rayanlecat https://www.rayanle.cat/lehack-2024-netexec-workshop-writeup/Twitter: https://x.com/mpgn_x64Ludus https://docs.ludus.cloud/docs/environment-guides/netexec-workshop-lehack-2024/
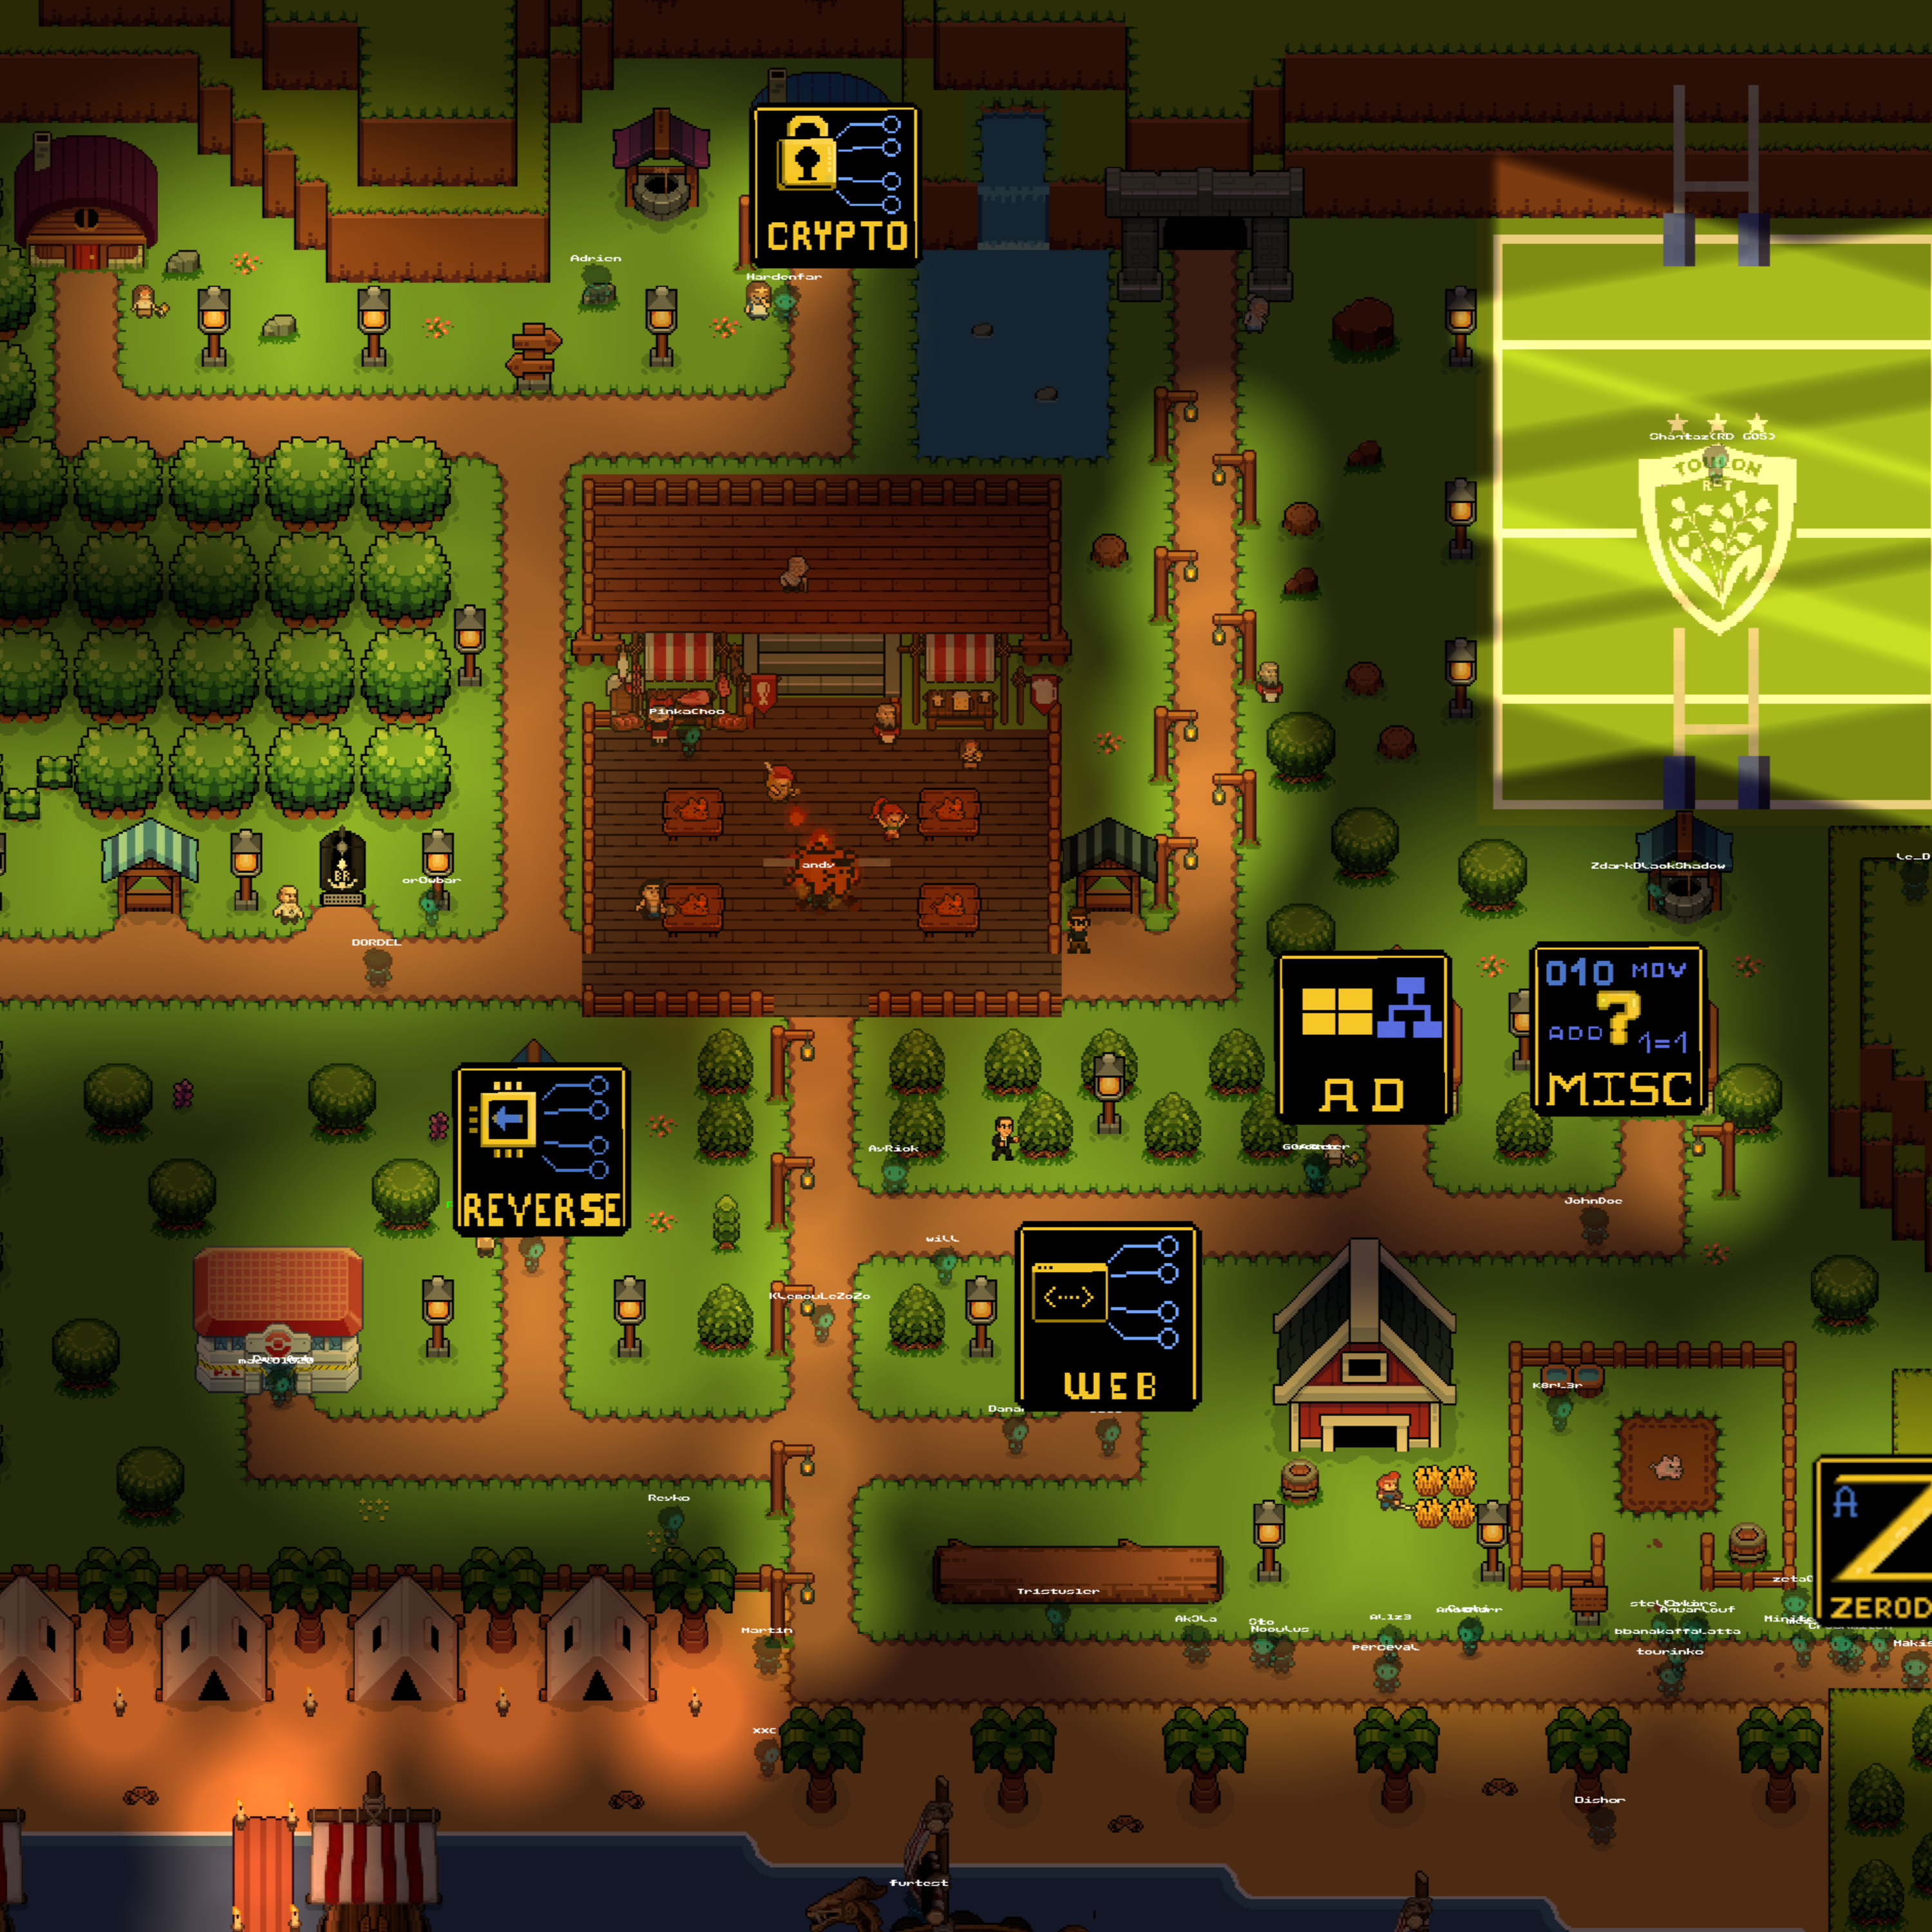
0x30 Un jeu, une quête, un ctf: l'aventure commence à barbhack
barbhack https://barbhack.fr/2025/fr/Twitter https://twitter.com/mpgn_x64

0x2F Doomer | Du bugbounty, de l'IA, un parcours atypique
Twitter: https://x.com/DoomerOutrunTwitter: https://x.com/mpgn_x64HackerOne https://hackerone.com/doomerhunter
0x2E Cravaterouge | Retour sur bloodyAD, une philosophie, badsuccessor
Twitter: https://x.com/mpgn_x64Twitter: https://x.com/rouge_cravateGithub bloodyad https://github.com/CravateRouge/bloodyADBlogpost: https://cravaterouge.com/articles/
0x2D @shadow_gatt | Démystification du redteam, des anecdotes
Twitter: https://x.com/shadow_gattTwitter: https://x.com/mpgn_x64Talk lehack https://www.youtube.com/watch?v=7itLKu4f1XQ
0x2C @croco_byte | Relai kerberos partie 2, SCCM, redteam !
Twitter: https://x.com/croco_byteTwitter: https://x.com/mpgn_x64Blog post - https://www.synacktiv.com/publications/relaying-kerberos-over-smb-using-krbrelayx- https://www.synacktiv.com/publications/abusing-multicast-poisoning-for-pre-authenticated-kerberos-relay-over-http-with- https://www.synacktiv.com/publications/taking-the-relaying-capabilities-of-multicast-poisoning-to-the-next-level-tric
0x2B Hugow | Du relai Kerberos, du redteam, de l'intrusion physique
Twitter: https://x.com/hugow_vincent
Twitter: https://x.com/mpgn_x64
Blog post https://www.synacktiv.com/publications/relaying-kerberos-over-smb-using-krbrelayx
0x2A jmbesnard | Retour sur la création d'AD_Miner, du graph, des perfs !
Twitter: https://x.com/jmbesnard_maz
Twitter: https://x.com/mpgn_x64
Adminer: https://github.com/Mazars-Tech/AD_Miner
Bluesky: mpgn
0x29 Worty | Retour d'expérience sur l'European CyberSecurity Challenge et le FCSC
Twitter: https://x.com/_worty
Twitter: https://x.com/mpgn_x64
ECSC: https://ecsc.eu/
FCSC: https://cyber.gouv.fr/france-cybersecurity-challenge-2024
HeroCTF: https://x.com/HeroCTF
0x28 poly & Vdehors | Hacking de Tesla, la pwn2own, des anecdotes
Twitter : https://x.com/_p0ly_
Twitter: https://x.com/vdehors
Twitter: https://x.com/mpgn_x64
0x27 Nabot & JahMyst | Retour sur la création de Secator, des études longues ou pas
Secator: https://github.com/freelabz/secator
Twitter: https://x.com/freelabz
Twitter: https://x.com/mpgn_x64
0x26 mrxch | Retour sur la création de Ghunt, une anecdote croustillante !
Twitter: https://twitter.com/mxrchreborn
Twitter: https://twitter.com/mpgn_x64
Ghunt : https://github.com/mxrch/GHunt
0x25 s4r | Du reverse, des anecdotes, la création de crackmes.one
Twitter https://twitter.com/sar5430
blog: https://sar5430.github.io/
Twitter https://twitter.com/mpgn_x64
Site de crackme: https://crackmes.one/
0x24 Arnaud Pilon | De la réponse à incident, retour d'expérience ...
Twitter https://twitter.com/nono_nonop
Twitter https://twitter.com/mpgn_x64
0x23 @fr0gger_ | Du threat Intel, de la réponse sur incident, le projet unprotect.io, un livre
Twitter fr0gger https://twitter.com/fr0gger_
Twitter https://twitter.com/mpgn_x64
Livre https://store.securitybreak.io/threatintel
Unprotect.io https://unprotect.it/https://unprotect.it/
0x22 - Renaud Feil | De la passion, de l'entreprenariat, une société: Synacktiv
Synacktiv: https://www.synacktiv.com/
mpgn: https://twitter.com/mpgn_x64
0x21 - @ringtail_sec | De l'hardware fait par un pentester pour les pentesters
ringtail twitter: https://twitter.com/ringtail_sec
ringtail site web: https://ringtail.ch/
basilisk: https://ringtail.ch/products/basilisk-zero-automatic-ethernet-ghosting
mpgn: https://twitter.com/mpgn_x64
Merci à la société BZHunt pour le prêt du matos https://bzhunt.fr/
0x20 - @BitK_ & @sakiirsecurity | Objectif top10 CtfTime, faire un bon ctf, les voyages, une anecdote croustillante
Twitter: BitK: https://twitter.com/BitK_
Twitter Sakiir: https://twitter.com/sakiirsecurity
Team CTFtime: https://ctftime.org/team/87434
mpgn: https://twitter.com/mpgn_x64
0x1F - @Zblurx | Retour sur dploot, certsync et le déchiffrement de Windows LAPS
Twitter: https://twitter.com/_zblurx
Github: https://github.com/zblurx
mpgn: https://twitter.com/mpgn_x64
0x1E - @Agarri_FR | Un peu d'histoire, la formation Mastering Burp Suite Pro, le bug bounty (XXE, XSLT, SSRF)
Twitter Agarri: https://twitter.com/Agarri_FR
Formation Burp Suite: https://hackademy.agarri.fr/
Twitter MasteringBurp : https://twitter.com/MasteringBurp
Blog Agarri : https://www.agarri.fr/fr
mpgn: https://twitter.com/mpgn_x64
0x1D - @palenath | De l'OSINT, un workshop à Interpol, de l'open source
palenath : https://twitter.com/palenath
Github: https://github.com/megadose/
Site OSINT FR: https://osintfr.com/
Discord OSINT FR: https://discord.gg/dWY9sWFKYD
Epios: https://epieos.com/
mpgn: https://twitter.com/mpgn_x64
0x1C - @Blaklis_ | Bug Bounty full time, un reward à 75k, la création du club Paris HackerOne
Blaklis_ : https://twitter.com/Blaklis_
Lien Club Paris Discord: https://discord.gg/MT6D8wP2Hd
Profil HackerOne: https://hackerone.com/blaklis?type=user
mpgn: https://twitter.com/mpgn_x64
0x1B - @M4yFly | Retour sur la création du lab GOAD et une RCE 9.8 sur GLPI CVE-2022-35914
M4Fly: https://twitter.com/M4yFly
GOAD: https://github.com/Orange-Cyberdefense/GOAD
RCE GLPI: https://mayfly277.github.io/posts/GLPI-htmlawed-CVE-2022-35914/
Arsenal: https://github.com/Orange-Cyberdefense/arsenal
Mindmap AD: https://github.com/Orange-Cyberdefense/ocd-mindmaps
mpgn: https://twitter.com/mpgn_x64
0x1A - @g0h4n | Retour sur la création de RustHound, l'outil crossplateforme plus rapide que Sharphound !
g0h4n: https://twitter.com/g0h4n_0
RustHound: https://github.com/OPENCYBER-FR/RustHound
SharpHound: https://github.com/BloodHoundAD/SharpHound
Bloodhound: https://github.com/BloodHoundAD/BloodHound
python-bloodhound: https://github.com/fox-it/BloodHound.py
mpgn: https://twitter.com/mpgn_x64
0x19 - @rkvl | Retour sur la création de Sliver & le redteam aux US (gilet pare balles non obligatoire)
lesnuages / rkervell : https://twitter.com/rkervell
Moloch : https://twitter.com/LittleJoeTables
blogpost sliver : https://dominicbreuker.com/
Sliver: https://github.com/BishopFox/sliver
mpgn: https://twitter.com/mpgn_x64
0x18 - @Swissky | Retour sur la création de PayloadsAllTheThings & SSRFmap !
mpgn: https://twitter.com/mpgn_x64
@pentest_swissky : https://twitter.com/pentest_swissky
PayloadsAllTheThings https://github.com/swisskyrepo/PayloadsAllTheThings
SSRFmap https://github.com/swisskyrepo/SSRFmap
0x17 - @_ZakSec | Retour sur la création de Masky et on parle purple team !
mpgn: https://twitter.com/mpgn_x64
@_ZakSec : https://twitter.com/_ZakSec
tool: https://github.com/Z4kSec/Masky
blog post: https://z4ksec.github.io/posts/masky-release-v0.0.3/
les coin cme: https://twitter.com/mpgn_x64/status/1537728466933714944?s=20&t=iq62ePRjV31FfNB8uk1x0w
0x16 - @snyff | Retour sur la création et la philosophie de PentesterLab
mpgn: https://twitter.com/mpgn_x64
@snyff: https://twitter.com/snyff
PentesterLab : https://pentesterlab.com/
0x15 - @Th3_l5D | Retour sur la création et la philosophie de NewbieContest
mpgn: https://twitter.com/mpgn_x64
@Th3_l5D: https://twitter.com/Th3_l5D
NewbieContent : https://www.newbiecontest.org/

0x14 - @T00uF | Retour sur DonPAPI !
mpgn: https://twitter.com/mpgn_x64
@T00uF : https://twitter.com/T00uF
github: https://github.com/login-securite/DonPAPI : Dumping revelant information on compromised targets without AV detection
recherche @Fist0urs pour Synacktiv https://www.synacktiv.com/ressources/JSSI_2017_DPAPI_Synacktiv.pdf
Hors-serie : Debrief du Workshop CrackMapExec (difficulté facile) à leHack 2022
Solution du lab présenté lors du Workshop CrackMapExec à leHack 2022 par @mpgn_x64
0x13 - @swapgs | One vulnerability to rule them all, nomination aux pwnie awards, première participation à la pwn2own
mpgn: https://twitter.com/mpgn_x64
@swapgs: https://twitter.com/swapgs
blog: https://swap.gs/
0x12 - the-useless-one & @lowercase_drm | Retour sur la librairie Pywerview
mpgn: https://twitter.com/mpgn_x64
the-useless-one (Yannick): https://github.com/the-useless-one
pywerview: https://github.com/the-useless-one/pywerview
@lowercase_drm (Simon) https://twitter.com/lowercase_drm
Le blog de l'équipe : https://offsec.almond.consulting/
0x11 - 0xLupin | Un parcours atypique, gagner la coupe du monde de Bug Bounty organisée par @Hackerone
mpgn: https://twitter.com/mpgn_x64
0xLupin: https://twitter.com/0xLupin
Classement final: https://twitter.com/Hacker0x01/status/1496962484204408837
Equipe:
arsene_lupin
adibou
kuromatae
yanzax
neolex
sehno
0xbeefed
bitk
bask
hisxo
reeverzax&
0x10 - Qazeer & th3m4ks | Retour sur l'outil EDRSandBlast, fonctionnement et contournement d'un EDR
mpgn: https://twitter.com/mpgn_x64
Qazeer: https://twitter.com/_Qazeer
th3m4ks: https://twitter.com/th3m4ks
Github: https://github.com/wavestone-cdt/EDRSandblast
Misc: https://connect.ed-diamond.com/misc/misc-118/techniques-de-contournement-de-la-supervision-des-edr
0x0F - Laluka | RCE sur root-me.org, recherche de 0-day et dev d'outils custom
mpgn: https://twitter.com/mpgn_x64
laluka: https://twitter.com/TheLaluka
Github: https://github.com/laluka/jolokia-exploitation-toolkit
Blog: https://thinkloveshare.com/
0x0E - Podalirius | Retour sur LDAPMonitor, pydsinternals et le rebuild d'un AS400
Liens:
mpgn: https://twitter.com/mpgn_x64
podalirius: https://twitter.com/podalirius_/
Github: https://github.com/p0dalirius
Blog: https://podalirius.net/en/
0x0D - Amat Cama | Gagner la Pwn2Own avec @fluoroacetate, la sth4ck, "w3challs c'est mieux que root-me !"
Twitter:
mpgn: https://twitter.com/mpgn_x64
Amat Cama: https://twitter.com/amatcama
fluoroacetate: https://twitter.com/fluoroacetate
https://sthack.fr/
https://www.root-me.org/
https://w3challs.com/challenges/list/pwn
Vainqueur de la Pwn2Own:
pwn2own Tokyo 2018 - Master of Pwn
pwn2o
0x0C - Shutdown | Retour sur Exegol / thehacker.recipes (partie 2)
Twitter:
mpgn: https://twitter.com/mpgn_x64
Shutdown: https://twitter.com/_nwodtuhs
Github project:
https://github.com/ShutdownRepo/pywhisker
https://github.com/ShutdownRepo/targetedKerberoast
https://github.com/ShutdownRepo/Exegol
https://www.thehacker.recipes/
https://github.com/koutto/pi-pwnbox-rogueap
0x0B - Shutdown | Retour sur les outils pywhisker / targetedKerberoast (partie 1)
Twitter:
mpgn: https://twitter.com/mpgn_x64
Shutdown: https://twitter.com/_nwodtuhs
Github project:
https://github.com/ShutdownRepo/pywhisker
https://github.com/ShutdownRepo/targetedKerberoast
https://github.com/ShutdownRepo/Exegol
https://www.thehacker.recipes/
https://github.com/koutto/pi-pwnbox-rogueap
0x0A - cfreal_ | Retour sur PHPGGC, du code, encore du code
Twitter:
mpgn: https://twitter.com/mpgn_x64
cfreal_: https://twitter.com/cfreal_
Github project:
PHPGGC: https://github.com/ambionics/phpggc
0x09 - topotam | Une belle histoire, du TII et PetitPotam
Twitter:
mpgn: https://twitter.com/mpgn_x64
topotam : https://twitter.com/topotam77
Github project:
PetitPotam: https://github.com/topotam/PetitPotam
0x08 - gentilkiwi | Retour sur kekeo, du RDP, de la smartcard et le choix de l'open source (partie 2)
Twitter:
mpgn: https://twitter.com/mpgn_x64
gentilkiwi: https://twitter.com/gentilkiwi
Github project:
Mimikatz: https://github.com/gentilkiwi/mimikatz
Kekeo: https://github.com/gentilkiwi/kekeo
0x07 - gentilkiwi | Retour sur Mimikatz, la BlueHat et les EDR ԅ(≖‿≖ԅ) (partie 1)
Twitter:
mpgn: https://twitter.com/mpgn_x64
gentilkiwi: https://twitter.com/gentilkiwi
Github project:
Mimikatz: https://github.com/gentilkiwi/mimikatz
Kekeo: https://github.com/gentilkiwi/kekeo
0x06 - vletoux | Retour sur PingCastle, le choix de l'open source et Mimikatz (dcsync)
Twitter:
mpgn: https://twitter.com/mpgn_x64
vletoux: https://twitter.com/mysmartlogon
Github project:
PingCastle: https://github.com/vletoux/pingcastle
NULL DACL youtube.com/watch?v=KILnU4FhQbc
GidsApplet: https://github.com/vletoux/GidsApplet
0x05 - lgandx | Retour sur Responder, du sponsoring via Patreon et PCredz
Twitter:
mpgn: https://twitter.com/mpgn_x64
lgandx: https://twitter.com/PythonResponder
Github projects:
Responder: https://github.com/lgandx/Responder
PCredz: https://github.com/lgandx/PCredz
Sponsoring via Patreon:
https://www.patreon.com/PythonResponder
https://www.paypal.com/paypalme/PythonResponder
Blog:
https://g-laurent.blogspo
0x04 - hisxo | Bug Bounty, motivex, moraline et un outil nommé gitGraber (partie 2)
Twitter:
mpgn: https://twitter.com/mpgn_x64
hisxo : https://twitter.com/adrien_jeanneau
Github projects:
gitGraber: https://github.com/hisxo/gitGraber
0x03 - hisxo | Bug Bounty, motivex, moraline et un outil nommé gitGraber (partie 1)
Twitter:
mpgn: https://twitter.com/mpgn_x64
hisxo : https://twitter.com/adrien_jeanneau
Github projects:
gitGraber: https://github.com/hisxo/gitGraber
0x02 - itm4n | Recherche de 0days Windows, trois outils, un blog (partie 2)
Twitter:
mpgn: https://twitter.com/mpgn_x64
itm4n: https://twitter.com/itm4n
Blog:
https://itm4n.github.io/
Github projects:
PrivescCheck: https://github.com/itm4n/PrivescCheck
FullPowers: https://github.com/itm4n/FullPowers
PrintSpoofer: https://github.com/itm4n/PrintSpoofer
0x01 - itm4n | Recherche de 0days Windows, trois outils, un blog (partie 1)
Twitter:
mpgn: https://twitter.com/mpgn_x64
itm4n: https://twitter.com/itm4n
Blog:
https://itm4n.github.io/
Github projects:
PrivescCheck: https://github.com/itm4n/PrivescCheck
FullPowers: https://github.com/itm4n/FullPowers
PrintSpoofer: https://github.com/itm4n/PrintSpoofer

0x00 - Pixis | Retour sur lsassy et hackndo.com
Twitter:
mpgn: https://twitter.com/mpgn_x64
Pixis: https://twitter.com/HackAndDo
Github projects:
lsassy: https://github.com/Hackndo/lsassy
pyGPOAbuse: https://github.com/Hackndo/pyGPOAbuse
sprayhound: https://github.com/Hackndo/sprayhound
Crackmapexec: https://github.com/byt3bl33d3r/CrackMapExec
Impacket: https://github.com/SecureAuthCorp/impacket
Prodump modul
Recommandé
Ma Psy M'a Dit
Lâche-toi la grap' !
✮✮✮ Mme GAULTIER ✮✮✮
Amour Fou par Camille Laurens
Français par Passion
MANIPURA - Spiritualité & Énergétique
Le Chant de la Terre
Français dans le Monde (FDLM)
Passeurs et Reveurs des mots

Les Aventures d'Ulysse

Le Bureau de l'étrange - ( HISTOIRES D'HORREUR - CREEPYPASTAS - HISTOIRES AUDIOS)
PIA – Podcast Intelligence Artificielle
